projects / 01 of 07
Phobos
Network intrusion detection on a 1 GB Raspberry Pi. Won Hashcode 12.0.
What it is
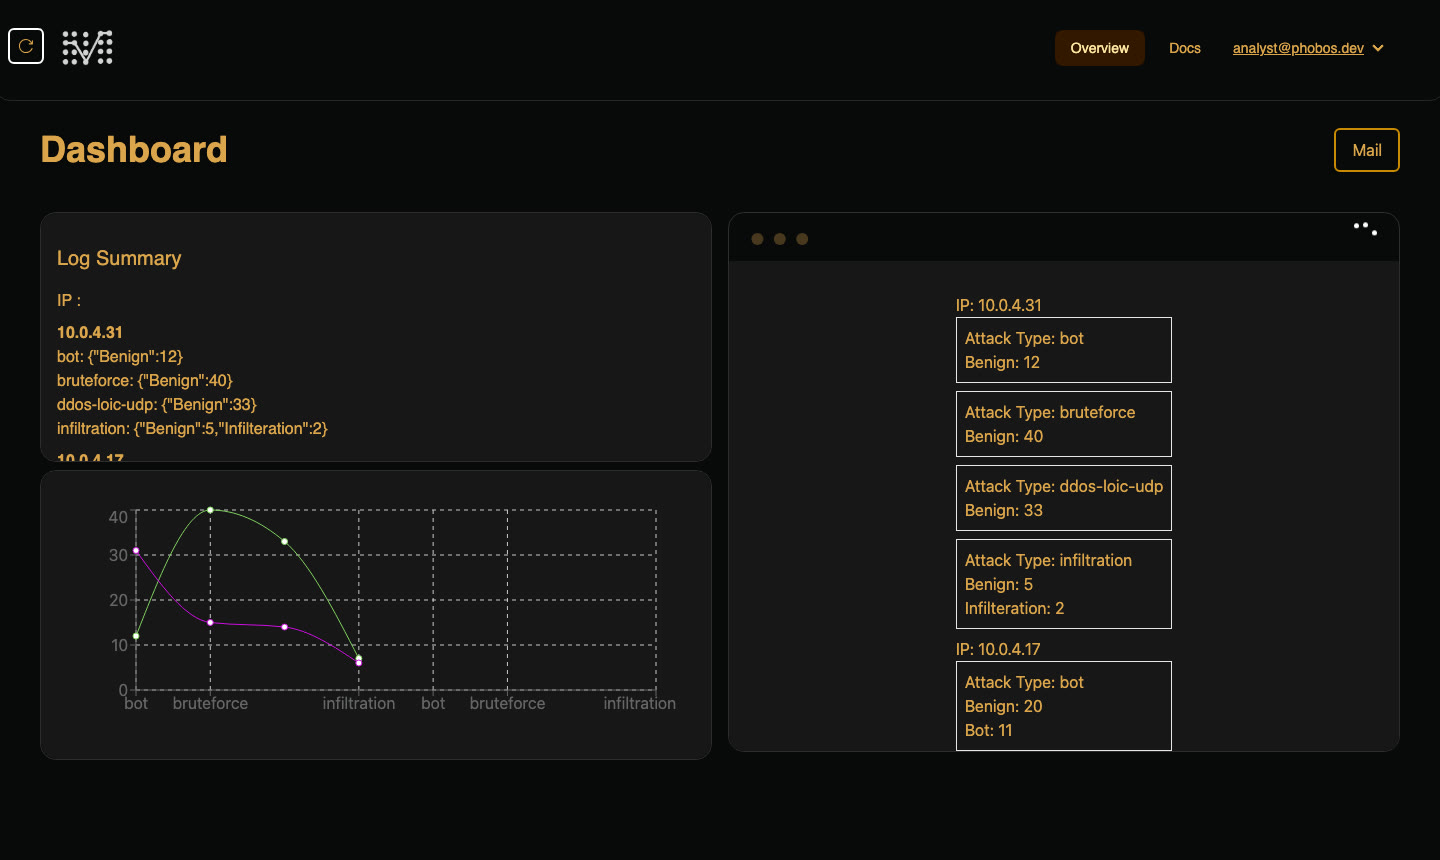
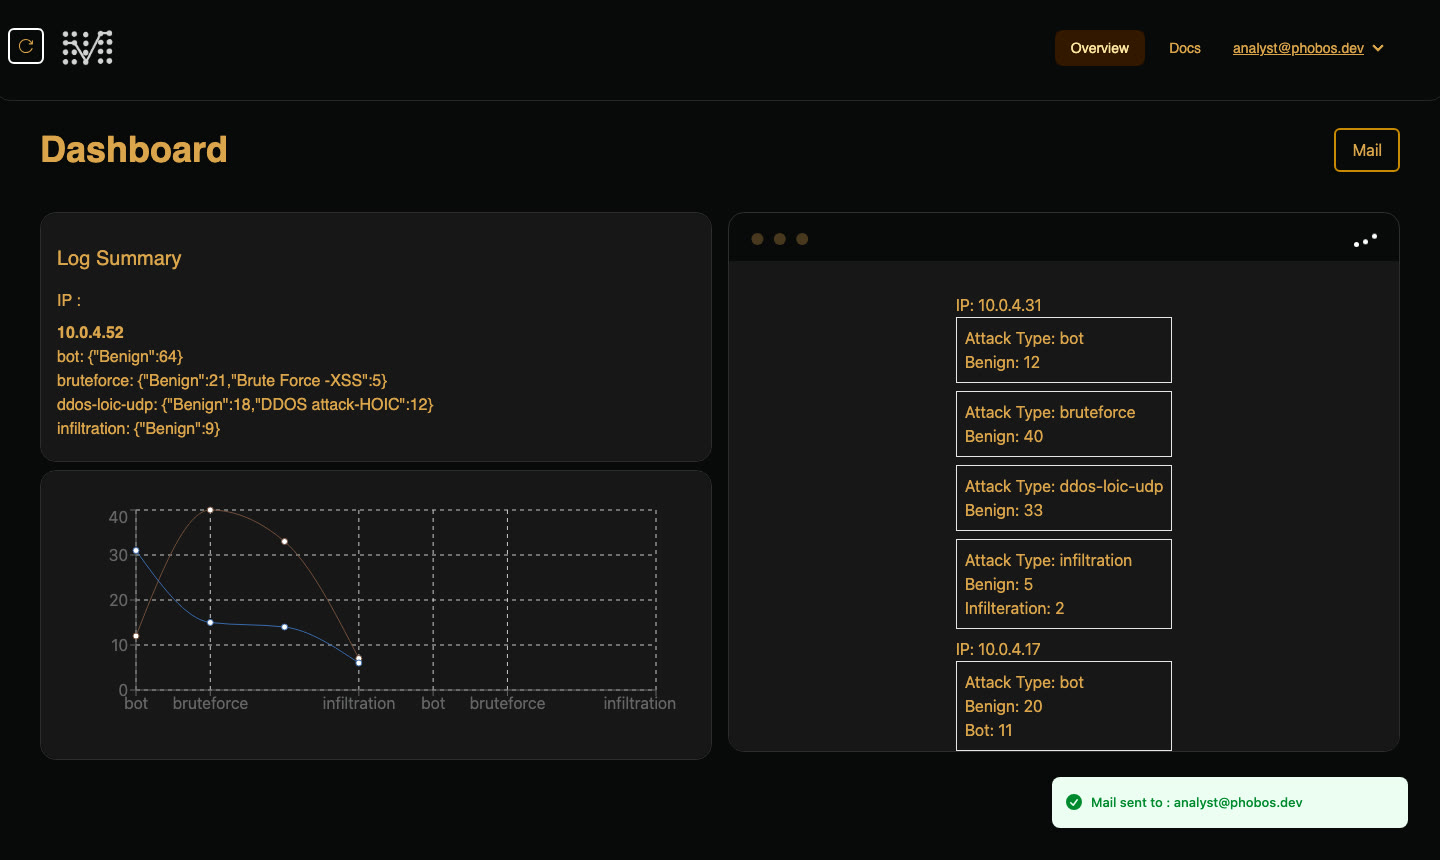
A network intrusion detection system small enough to run on a 1 GB Raspberry Pi. It watches network flow logs and flags bot traffic, brute-force and SQL-injection attempts, DDoS floods and infiltration, per machine, as they happen.
How it works
Flow logs are streamed over MQTT into an ML engine: four XGBoost models, one per attack family, each trained on its own day of labelled network-flow captures and classifying every flow as benign or as its attack. Results are grouped by IP on a React dashboard, and an alert can be mailed to the analyst from there.
Alongside it sits a small command-and-control server in Go for registering agents and managing access. It won Hashcode 12.0.
Gallery